We assess internet-facing systems and services to identify vulnerabilities that could be exploited by external attackers.
Review exposed websites, APIs, customer portals, login pages, and internet-facing application vulnerabilities.
Identify exposed hosts, open ports, perimeter services, TLS issues, and externally accessible vulnerabilities.
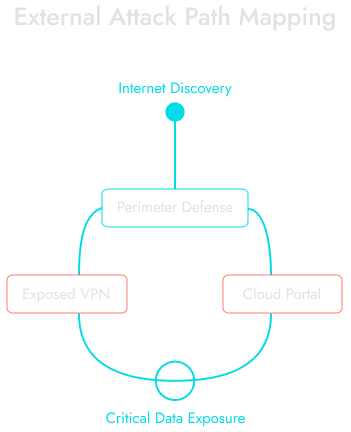
Assess VPN, RDP, SSH, SSO, admin portals, MFA weaknesses, and exposed remote-access entry points.
Analyze public cloud workloads, storage, management interfaces, public endpoints, and misconfigured cloud access.
Misconfigured internet-facing services create unnecessary exposure.
Weak remote access and perimeter controls increase attack opportunities.
Exposed credentials, admin panels, and public assets expand the attack surface.
Discover externally accessible assets before attackers do through proactive assessment.
Assess perimeter services, remote access infrastructure, cloud exposure, APIs, and public-facing applications.
Prioritize remediation based on realistic external attack paths and business risk.
A structured methodology designed to uncover externally exploitable vulnerabilities across internet-facing environments.
Identify exposed assets and define external attack scope.
Gather public intelligence and map attack surfaces.
Assess internet-facing services and applications.
Validate findings through controlled external testing.
Deliver prioritized remediation guidance.
We assess externally accessible VPNs, secure gateways, remote access portals, and authentication controls.
Identify internet-facing services vulnerable to attacks using publicly known vulnerabilities actively targeted by modern threat actors.
Overlooked or forgotten domains, subdomains, and internet-facing assets that increase the organization's external attack surface.
Analyze exposed storage, cloud workloads, public endpoints, management interfaces, and access controls.
Exposed panels, SSH, VPN, RDP, management ports, and admin interfaces.
Internet-facing services running unsupported or outdated software versions.
Exposed usernames, passwords, API keys, and authentication secrets discovered across public sources.
“We engaged 7ASecurity to do a code audit of a number of our internal products at the Linux Foundation. The 7ASecurity team quickly identified a number of insightful recommendations, including guidance on how to resolve the most and least critical security vulnerabilities. 7ASecurity definitely knows what they're doing and made securing our applications a breeze. We left the engagement confident about our security, and ready to work with them again for future security audits."
Rudy Grigar, Senior Manager of Technology Services The Linux Foundation
“The Linux Foundation had the privilege of working with the 7ASecurity team during a comprehensive security audit of the Linux Foundation platform. Their expertise and thorough approach were evident from the start. Thanks to their diligent efforts, we successfully addressed several security vulnerabilities, reinforcing the integrity of our platform. We highly recommend 7ASecurity for their exceptional skills and commitment to enhancing digital security."
David Deal, Director of Platform The Linux Foundation
“7ASecurity has been an exemplary resource for OSTIF time and time again. They've assisted us with large and complicated projects with the Linux Foundation and Mozilla that required specific technical acumen. They've always adapted to the unique challenges that our open source projects face with tenacity, and their experience and professionalism bring us fantastic results."
Derek Zimmer, Executive Director Open Source Technology Improvement Fund (OSTIF)
“OSTIF and 7ASecurity were amazing partners that provided a helpful guiding hand, and made the process of doing the audit a breeze. We really appreciated their professionalism and expertise. I can confidently say that we plan on working with them again."
Ryan Sipes, Thunderbird's Product and Business Development Manager Mozilla Foundation
“Engaging 7ASecurity for our audit was a key move for Bridgefy. They expertly navigated our code and services, uncovering vulnerabilities and offering solutions that refined our approach to safeguarding data and ensuring privacy.
Their hard work enabled a significant enhancement in the resilience of our products. Each insight they provided was a golden opportunity to further our mission of creating reliable, Internet-independent communication.
Thanks to 7ASecurity, we’re now more confident in the robustness of our services and feel empowered to continue our journey to change the world. We’d readily recommend their stellar work to any tech firm that values user protection above all else. To sum it up, their expertise has brought a remarkable boost to our security measures."
Jorge Ríos, CEO Bridgefy
“Our experience with 7ASecurity during the security audit was nothing short of remarkable. Their team of seasoned professionals managed to identify vulnerabilities that had even our in-house experts astounded. Throughout the course of the audit, we eagerly anticipated their insights and findings, knowing that each one was a step towards strengthening our defenses.
The 7ASecurity team displayed extraordinary diligence and expertise, and their contributions have greatly enhanced the security of ArgoVPN. As a result of their diligent efforts, we are now more equipped than ever to serve our Iranian customers with the assurance that we are mitigating major security concerns effectively.
We express our heartfelt gratitude to 7ASecurity for their exceptional work. Their audit has significantly increased our confidence in the safety of our services, and we would highly recommend their services to any organization that values robust security."
Nariman Gharib, ArgoVPN
“7ASecurity was great to work with. The test team was super fast and communicated very well. I would fully recommend 7ASecurity to anybody looking for a high quality penetration test."
Luke Shipley, Director Zinc Work Limited
“Working with 7ASecurity was a pleasure. Communications were clear and consistent throughout the engagement. 7ASecurity took the time to understand the issues and threats faced by Psiphon’s anti-censorship technology and thoroughly investigated our recently developed, cutting-edge circumvention enhancements. I highly recommend 7ASecurity and hope to work with Abraham and his team again."
Jessica Wever, Project Manager Psiphon Inc
“7ASecurity are an extremely well accomplished Technology Security outfit. They have been instrumental in bolstering our Defences with both passive and reactive strategic thinking. In addition their tactical and tool knowledge is deep and broad. We have also engaged them for some bespoke Development and QA security training. Polite, courteous and great listeners they do not try and sell a one size fits all solution - recommended."
Paul Broome, CTO Northgate Public Services Limited (NPS)
“7ASecurity delivered the best pentest we've had so far. They were very responsive throughout the whole assessment and provided a clear report with detailed findings and recommendations. They have a team of skilled professionals who will test your web application very thoroughly."
Jindrich S, Security Manager ProductBoard
“I am extremely grateful to Abraham and his team at 7ASecurity for the exemplary service they provided us on a recent penetration testing project. They were professional, non-intrusive and highly diligent in all their investigations and provided detailed recommendations from which we were able to immediately act upon. We look forward to working with you again in the future."
James Cundle, CTO Mio
“Really appreciated working with 7ASecurity. They were both professional and flexible, providing us with the expertise required to improve and the patience to help us with it. They didn't just stop at providing us the results either, but took the time to train our team and help us understand various problems from different angles in order to truly leave us off better informed at the end of the process."
Joshua Wöhle, CTO SuperAwesome
“7ASecurity helped us to successfully complete customers’ security assessments. Their knowledge of the mobile applications ecosystem and technical background was a key point to perform penetration tests against mobile applications dealing with sensitive data (financial, healthcare). Our collaboration was smooth, efficient and we hope to continue to work together in the future."
Xavier Mertens, CEO Xameco SRL
“7ASecurity developed a unique course for eLearnSecurity with Practical Web Defense: This focuses on both attacking and defending Web Applications unlike the traditional courses which focus only on attacking applications. Students not only learn how to exploit the application but also learn to patch the vulnerabilities and block the attacks which is a complete 360 degree learning of web security. The coherent teaching style of 7ASecurity and the associated labs strikes a perfect balance between theory and practical. Hands down, eWDP is a course with a difference!"
Anirudh Anand, Security Analyst Flipkart
“I’d like to thank OTF and 7ASecurity – working with them for this audit was both a pleasure and really useful for the DEfO project team. Doing audits like this for code to be contributed to important upstream projects like OpenSSL is a really good plan and I look forward to the next phase when we do an audit for the full ECH code."
Dr. Stephen Farrell, One of the DEFO developers Trinity College Dublin and Tolerant Networks Ltd
Identify exploitable vulnerabilities before they impact your business. Schedule a comprehensive External Penetration Test and receive clear, actionable findings to strengthen your internet-facing systems, applications, infrastructure, and remote access services.

Evaluate internet-facing applications, APIs, network infrastructure, VPNs, remote access services, cloud-exposed assets, public endpoints, and external attack paths to identify vulnerabilities and unnecessary exposure.

Receive a prioritized report with proof of exploitation, business impact, risk ratings, and practical remediation guidance to help your team reduce external exposure and strengthen your security posture.

